[go: up one dir, main page]

Navigating the EU’s Cyber Resilience Act (CRA)? Get our free eBook.

Free eBook
The Open Source Security Foundation (OpenSSF) is a community of software developers, security engineers, and more who are working together to secure open source software for the greater public good.

Collaborate on capabilities and best practices that secure open source software.

Participate in the latest community conversations and engage with experts.

Take free courses on secure coding practices as part of our certificate program.

Explore our helpful security guides to help secure your project from the start.

OpenSSF Hosted Events

OpenSSF events are a great opportunity to get involved with the OpenSSF community across the security and open source ecosystem. Join us and share ideas, progress, and collaborate on securing open source software.

Read the Latest Reports From OpenSSF
2026 CRA Awareness and Readiness Report

CRA Awareness and Readiness Report

Securing Open Source in the Age of AI

Securing Open Source in the Age of AI

Gemara: A Governance, Risk, and Compliance Engineering Model for Automated Risk Assessment

Gemara: A Governance, Risk, and Compliance Engineering Model for Automated Risk Assessment

Recent Blog Posts
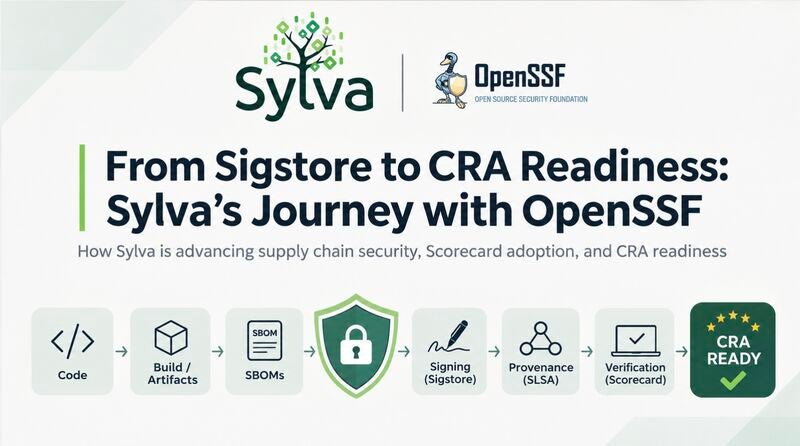
BlogGuest BlogFrom Sigstore to CRA readiness: Sylva’s journey with OpenSSF
November 6, 2026

From Sigstore to CRA readiness: Sylva’s journey with OpenSSF

Sylva’s security work relies heavily on the OpenSSF ecosystem. From supply chain tooling with Sigstore and SLSA to adopting OpenSSF Scorecard and Best Practices badges, learn how Sylva is approaching…
BlogCase StudiesCase Study: Kubescape Completes All Six Security Slam Badges with OpenSSF
November 5, 2026

Case Study: Kubescape Completes All Six Security Slam Badges with OpenSSF

Kubescape completed all six project-level badges in the Fall 2026 Security Slam, bringing maintainers and community contributors together to strengthen security across its open source Kubernetes platform. Learn how 150+…
BlogGuest BlogThe PHP Security Wake-Up Call: Fixes Are Only the Beginning
November 3, 2026

The PHP Security Wake-Up Call: Fixes Are Only the Beginning

By Jeff Borek and Mike LinksvayerRecent PHP vulnerabilities highlight why open source security requires sustained investment and action from everyone who builds on it. PHP, an open source programming language,…

Open source software is pervasive in data centers, consumer devices, and applications. Securing open source software requires fostering collaboration, establishing best practices, and developing innovative solutions.

Join the growing list of organizations supporting the advancement of securing open source technology and funding the development and adoption of OpenSSF initiatives.

Explore Membership in OpenSSF